Cloud native platforms increasingly execute code their operators did not write and cannot fully trust. AI agents generate Python on demand, customers upload plug-ins, data teams define user functions, and model-training systems run thousands of candidate programs. Containers can package those workloads, but packaging is not the same as a hard security boundary. Full virtual machines provide a stronger boundary, yet their boot and management costs have traditionally made them awkward for short-lived, fine-grained tasks.
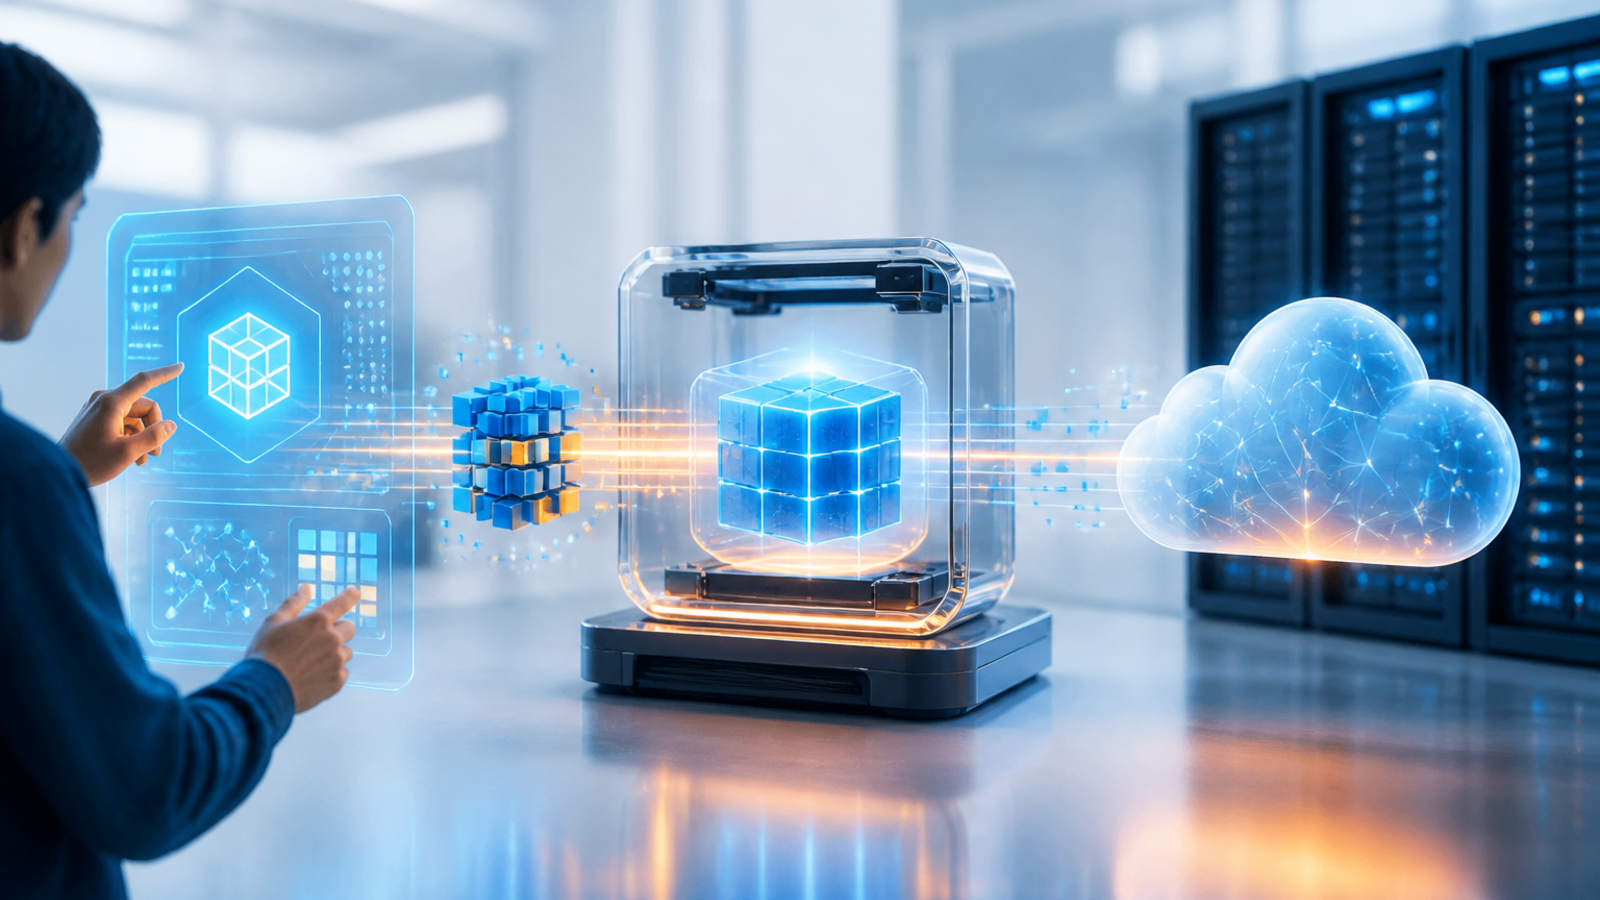
Hyperlight, a CNCF Sandbox project, is testing a middle path. Its new hyperlight-unikraft layer can run ordinary Linux binaries inside embedded micro-VMs, while snapshots keep warm-start latency in the millisecond range. The important change is not simply that another micro-VM exists. It is that platform builders can apply a hypervisor boundary at the scale of an individual function, agent step, database UDF, or Kubernetes workload without first porting that code to a specialized guest SDK.
Why ordinary Linux support changes the proposition
The original Hyperlight model is deliberately narrow. An application embeds the Rust-based virtual machine monitor as a library, loads a purpose-built guest, and communicates with it through typed host and guest function calls. The guest has no general-purpose operating system, and access to host resources is denied unless the embedding application exposes a capability. That design minimizes overhead, but it also asks developers to build for Hyperlight’s guest environment.
Hyperlight-unikraft expands the addressable workload by inserting a Unikraft unikernel as the guest kernel. The result can execute the same Linux binaries teams already use, including Python, Node.js, .NET, Java, PHP, Go, Rust, C, Bash, PowerShell, QuickJS, and Wasmtime workloads. It supports x86-64 and Arm64 hosts, with KVM or MSHV on Linux, Windows Hypervisor Platform on Windows, and Hypervisor.framework on Apple silicon.
That compatibility is the project’s most consequential feature. A team can start from published runtime images, extend a root filesystem with an ordinary Dockerfile, and install packages through familiar language tooling. The hluk CLI builds and runs the guest, while the Rust library exposes the same sandbox construction, execution, snapshot, and restore primitives to applications. The project is no longer limited to code written specifically for Hyperlight; it can sit underneath existing language ecosystems.
The security model is capability-first
Each sandbox has memory isolated through hardware virtualization. Unlike a conventional VM, it does not emulate a broad set of devices. The guest cannot see host files or use the network by default. The embedder explicitly grants mounts, network access, listening ports, or callable host functions. This default-deny design matters because untrusted execution is frequently compromised by an overlooked permission rather than a novel isolation primitive.
The distinction from a container is material. Containers isolate processes while sharing the host kernel; a kernel vulnerability can therefore undermine the boundary. A Hyperlight guest sits behind the host hypervisor, so an escape from a language runtime or inner software sandbox still encounters a separate hardware-enforced boundary. The project demonstrated this layered defense with a previously fixed Wasmtime vulnerability: code that could read beyond the WebAssembly sandbox was confined to the micro-VM’s memory rather than reaching secrets in the host process.
This does not make arbitrary code risk-free. Hypervisors, the VMM, guest kernel, and intentionally exposed host functions all remain part of the trusted computing base. Network access and writable mounts can also create application-level escape routes even when the VM boundary holds. Platform teams still need image provenance, patching, resource limits, audit trails, and careful capability review. Hyperlight narrows the blast radius; it does not eliminate operational security work.
Snapshots attack the real cold-start cost
Micro-VM discussions often focus on boot time, but an operating-system boot is only one part of application startup. Python imports modules, .NET invokes a JIT compiler, Java initializes a runtime, and frameworks load dependency graphs before user code begins. Hyperlight-unikraft warms the guest once, pauses it at an application-defined ready point, and saves its memory state. Future invocations restore that state instead of repeating initialization.
The project’s published benchmark illustrates both the opportunity and the limit. On an eight-vCPU Azure VM using nested KVM and hluk 0.20.1, a snapshot-restored Python hello-world took a median 22 milliseconds versus 17 milliseconds natively. Node.js hello-world took 39 milliseconds versus 22 milliseconds. For trivial programs, fixed virtualization costs still lose.
Heavier initialization reverses the result. A C# source workload compiled inside the guest by Roslyn completed in 95 milliseconds from a snapshot, compared with 1,549 milliseconds for dotnet run. A Python script importing NumPy, pandas, and scikit-learn took 45 milliseconds from the snapshot versus 1,119 milliseconds natively. These are project-reported results from one configuration, not universal performance guarantees, but they show why the design is relevant: snapshots amortize the startup work that modern language runtimes actually perform.
The architectural benefit is consistent across languages. V8 snapshots or Java CRaC can accelerate specific runtimes, whereas a VM snapshot can capture a prepared interpreter, libraries, and application state through the same mechanism. Multiple sandboxes can also restore from a common warm image. That makes strong isolation more plausible for bursty functions and agent actions where starting a traditional VM per request would be impractical.
Kubernetes integration keeps the abstraction familiar
Hyperlight-unikraft is not positioned as a replacement for Kubernetes or containerd. The urunc integration packages a guest as an OCI image and runs it through containerd. Kubernetes can select that runtime with a RuntimeClass, and the image may include a warm snapshot so the workload resumes instead of cold-booting. The approach preserves scheduling, image distribution, and pod-oriented operations while changing the isolation boundary underneath the container interface.
That layering is strategically important. A novel sandbox is much easier to adopt when platform teams do not have to invent a new deployment control plane. Existing policy can decide which workloads receive the alternate runtime, and teams can begin with a narrow class of risky jobs rather than migrating an entire cluster. Agent Sandbox integration offers another route: a warm pool can fulfill a claimed Kubernetes sandbox with a snapshot-backed Hyperlight runtime.
Operators should still treat this as an emerging runtime path. Hyperlight’s main repository is explicitly pre-1.0, and APIs may change. Workload compatibility will not equal a full Linux VM in every corner, even though ordinary binaries run. On macOS, Hypervisor.framework permits one VM per process, so concurrency requires multiple processes. Support levels also differ across architectures and debugging features. Those constraints belong in an evaluation plan, not in a footnote.
Agent execution may be the strongest early use case
AI agents create a particularly difficult combination of requirements: code is generated dynamically, it often needs mainstream Python libraries, state may persist across several steps, and latency affects the interactive experience. A language-only sandbox is attractive until the runtime or one of its native extensions becomes the vulnerability. A conventional VM is defensible but expensive to create and reset at agent-step granularity.
Hyperlight-unikraft’s integrations show how snapshots can support several state models. Its smolagents executor keeps a micro-VM for a session and pauses it between steps. An MCP server exposes a Python execution tool whose variables survive across calls. An OpenAI Agents SDK provider instead restores a fresh micro-VM for each shell command while sharing only a controlled workspace. These are variations on the same primitive: platform designers can choose persistence or clean-room execution without abandoning the hypervisor boundary.
The pattern extends beyond agents. A ClickHouse integration runs Python user-defined functions in snapshot-restored micro-VMs, preventing one invocation from leaving guest state for the next. A verl integration executes code-reward test cases during model training with no network or host visibility, limiting a generated program’s ability to tamper with its score or training node. In all of these cases, the unit of isolation is much smaller than a long-running service.
What platform teams should validate
Hyperlight is promising, but the right proof of concept is workload-specific. Teams evaluating it should measure the complete path rather than quoting a microbenchmark. A useful trial should answer:
- Compatibility: Does the real binary, native extension, filesystem behavior, clock, randomness source, and networking pattern work under the selected guest runtime?
- Latency distribution: How do cold boot, warm restore, steady execution, and teardown behave at the 50th, 95th, and 99th percentiles under concurrency?
- Memory economics: How much private memory does each restored guest consume, and how effectively can prepared state be shared?
- Capability design: Can mounts be read-only, destinations allow-listed, and host functions kept narrow enough that a compromised guest has little useful reach?
- Operations: Are logs, metrics, traces, crash diagnostics, image scanning, patch rollout, and incident response adequate for production ownership?
The first candidates should be jobs with high trust risk, meaningful runtime initialization, and short execution windows: generated-code tools, customer plug-ins, build steps, data UDFs, or evaluation harnesses. A simple stateless service that already starts instantly in a conventional container may gain little. The technology has the most leverage where teams currently choose between weak isolation and unacceptable startup overhead.
A smaller unit of hard isolation
Hyperlight-unikraft does not erase the tradeoffs among containers, software sandboxes, micro-VMs, and full VMs. It changes where one point on that curve sits. Ordinary Linux compatibility reduces porting cost, capability-based access limits what a guest receives, and snapshot restore targets the initialization delays that dominate many modern runtimes.
For Kubernetes and cloud native teams, the larger implication is that hypervisor isolation can become a per-task platform capability rather than a separate infrastructure tier. If the project matures, a RuntimeClass, agent executor, or database engine could request a disposable hardware boundary as routinely as it now requests a container. That is a meaningful shift—but pre-1.0 status and uneven platform constraints make disciplined testing essential before production adoption.